ONGOING OT CYBERSECURITY
Ongoing OT cybersecurity.
Built around production.
Zeroday Cybersecurity provides ongoing operational technology (OT) cybersecurity services and managed OT vulnerability management for manufacturing, industrial facilities and mining.
Turn security priorities into clear responsibilities, actions and evidence your team can review. Start with a standalone assessment or bring existing findings to discuss ongoing support.
ONGOING OT SERVICES
Ongoing OT services
with clear ownership.
Keep OT security priorities, actions and evidence under regular review around the systems and processes that matter to production.
Define activities, responsibilities, review frequency and coverage with your team.
MANAGED OT VULNERABILITY MANAGEMENT
Managed OT vulnerability management.
Review which reported vulnerabilities apply, consider operational constraints and agree who owns treatment. Track the evidence behind each decision.
Make unresolved questions and implementation dependencies visible.
Focused OT cybersecurity projects
Address a defined need with a clear scope, agreed deliverables and responsibilities.
OT Finding-to-Closure Support
Bring open findings that need accountable action. Connect the requirement, evidence, treatment owner and remaining decision in a record your team can review.
Critical Process Recovery Readiness
Review one critical process to identify missing recovery materials, unclear responsibilities and untested steps.
Need to establish a baseline first? Explore an OT Security Assessment.
ILLUSTRATIVE OPERATING RECORD
What an OT service review records.
This fictional supplier-access example shows how a service record connects an operational question to owners, evidence and the next decision.
1. Operational Issue
Supplier support responsibilities changed for a production process. The site needs to review who owns the continuing access decision.
2. Evidence to Review
The current access inventory, provider handover record and internal approval responsibilities.
3. Accountable Participants
The site IT/OT owner, supplier and authorized operational approver review their responsibilities.
4. Coordinated Action
Confirm the continuing support need, identify missing evidence and agree who will follow through.
5. Current Status
Awaiting owner review. The access decision and evidence review remain open.
6. Next Decision
Approve the documented responsibility, request missing evidence or record an authorized exception.
Review again at the cadence agreed with the owner. Keep completed actions, missing evidence and unresolved dependencies distinct.
A clear status. Evidence behind it. An owner for what remains.
TWO WAYS TO START
Start with an assessment
or existing evidence.
An OT Security Assessment reviews a defined system, process or requirement. Receive an evidence record, prioritized gaps and recommended actions that have standalone value.
Already have a recent assessment, open findings or a recurring need? Bring the available evidence to discuss ongoing support. We will review what it can support and what additional information is needed.
Continuing service requires its own agreement. The scope defines activities, owners, cadence, boundaries and the decisions the service will support.
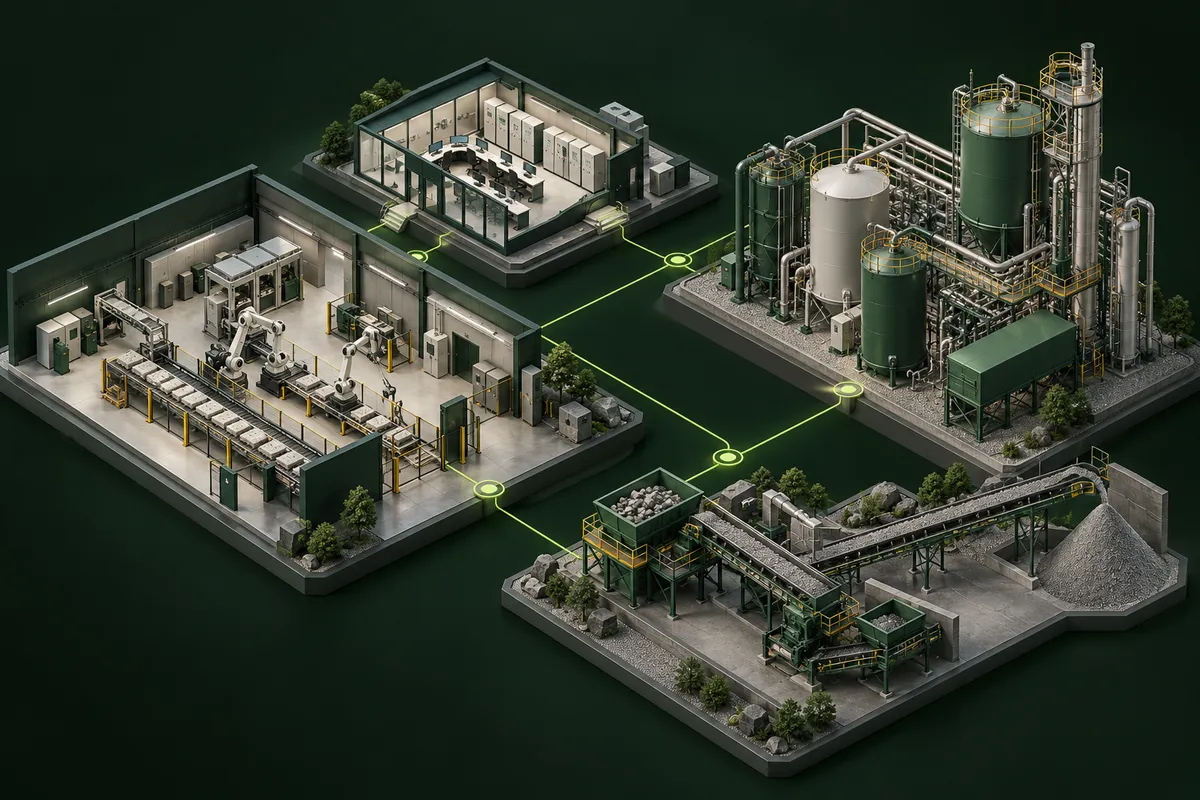
Illustrative operational model. Actual systems, dependencies and responsibilities are defined with your team.
BUILT FOR INDUSTRIAL OPERATIONS
OT cybersecurity for your industry.
CHOOSE YOUR OPERATING CONTEXT
Manufacturing: Production lines, cells and plant utilities, with customer requirements and equipment changes shaping the work.
Industrial facilities: Shared systems, supplier access and inherited responsibilities across technical providers.
Mining & mineral processing: Processing areas, upgrades and handovers with upstream, downstream and provider dependencies.
WHAT MAKES AN ONGOING SCOPE USEFUL
Bring a recurring OT security need, an internal sponsor and the technical owners of the affected operation or system. Together, we can define the work that needs continuing review and follow-through.
Zeroday works alongside operations, IT/OT, controls engineers and existing providers. Agree who reviews, acts and authorizes decisions.
FROM FINDINGS TO CONTINUING WORK
How ongoing OT service reviews work.
Use the baseline to agree priorities, responsibilities and review criteria. Your authorized site teams and technical providers retain control of live-system changes and equipment-specific procedures.
01 / UNDERSTAND
Establish
the Baseline
02 / DEFINE
Agree Scope
& Ownership
03 / CONTINUE
Review Progress
at the Agreed Cadence
THE PERSON LEADING THE RELATIONSHIP
Led by Andres Torres.
Founder and Executive Lead, Industrial Cybersecurity
Andres Torres brings enterprise OT cybersecurity leadership and more than two decades of cybersecurity and U.S. Marine Corps experience. His focus is turning technical uncertainty into clear priorities and practical operational decisions.
Andres leads the executive relationship and program direction. Technical review and specialist work are assigned according to the agreed scope and the qualifications required for your environment.
Company, Leadership and Buyer Resources
BUYER QUESTIONS
Questions about OT services.
What does the ongoing service include?
The agreed scope defines systems, activities, responsibilities, review cadence, coverage and escalation arrangements. Ongoing OT services and managed OT vulnerability management are available, with scope and cadence agreed per client.
Do we need an assessment first?
An assessment is a useful standalone entry. If you already have relevant findings or a defined recurring need, we can review that evidence and discuss an ongoing scope directly.
Who changes our live systems?
Your authorized site teams and technical providers retain control of live-system changes. Implementation responsibilities and equipment-specific work must be explicit in the agreed scope.
Can we buy a defined project?
Yes. OT Finding-to-Closure Support connects agreed findings to owners, actions and evidence. Critical Process Recovery Readiness reviews one process and its recovery dependencies. Each is separately scoped.
START WITH YOUR OPERATION
Let’s define the work
your team needs.
Tell us whether you need an assessment, ongoing OT support, vulnerability management or a defined project. Share a nonconfidential summary of the operational issue, the people involved and any decision timing.
We will review your inquiry and arrange a conversation about your priorities, responsibilities and the right scope of work.
1755 E Plumb Lane, Suite 150
Reno, Nevada 89502